Skip to content

Security testing

AI-fast. Human-proven.

Three headline tests and the classic pentests, each at a fixed price. AI maps and probes everything in scope in days; then a person proves each finding, tests what AI misses, and signs the report your auditor and customers will accept.

01 · For SOC 2, ISO 27001 and enterprise deals

Proof Pentest

AI covers your whole web app and API in days. Then a person tests every role and tenant by hand, proves each finding, and signs the report your auditor and customers will accept.

  • AI-driven mapping and coverage of the web app and its API
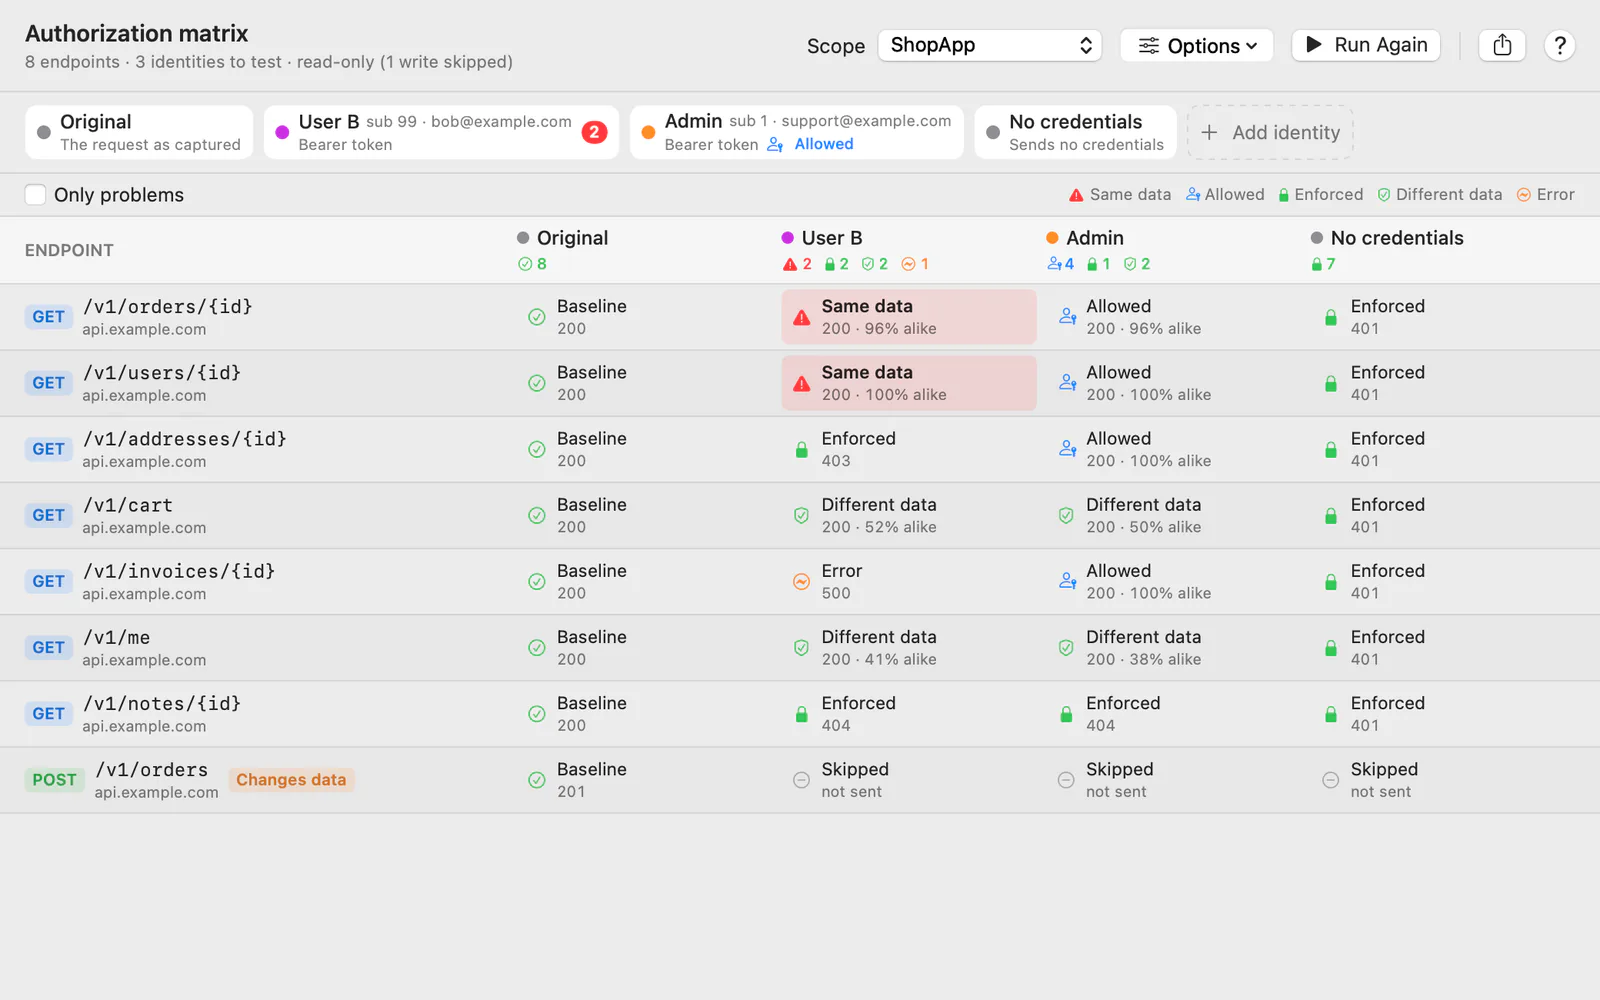
  • A role-by-role, tenant-by-tenant authorization (IDOR) matrix, built from captured traffic with Cloak Proxy
  • Human-led testing of sign-in, sessions, access control and business logic
  • Basic prompt-injection and data-leak checks on any AI feature in the app

$4,900–9,500≈€4,400–8,500≈£3,700–7,200≈CA$7,000–13,500≈A$7,000–13,600≈S$6,300–12,200≈AED 18,000–34,900from ₹95,000

Report in 5 working days
02 · For copilots, chat, RAG, agents and MCP

AI Feature Security Test

Can your AI feature be talked into leaking another customer's data, or into using its tools in ways you never meant? We test it the way attackers do, prove the answer, and sign it.

  • Direct and indirect prompt injection, through documents, web pages, email and tickets
  • Data leaking between customers, and system-prompt and secret exposure
  • Tool, function and MCP misuse, and what each agent is allowed to do
  • The 32 published agent-access checks: OAuth and token scopes on connectors and MCP servers

$6,500–18,000≈€5,800–16,100≈£4,900–13,600≈CA$9,200–25,600≈A$9,300–25,800≈S$8,300–23,000≈AED 23,900–66,100₹1,50,000–3,40,000

Added to a Proof Pentest: $2,500≈€2,200≈£1,900≈CA$3,600≈A$3,600≈S$3,200≈AED 9,200₹75,000

03 · After a supply-chain attack

Dev Environment Compromise Check

When the next npm, PyPI or AI-agent supply-chain attack hits, know within 48 hours whether it reached your developers' Macs, your CI or your secrets, then close the paths it used. Cloak Watch finds it; we fix it.

  • A sweep of developer Macs (with Cloak Watch) and CI for the incident's indicators of compromise
  • A review of lockfiles, CI logs and outbound traffic
  • A secret-rotation runbook, in the order that matters
  • A signed “affected” or “not affected” letter for customers and insurers

$4,500≈€4,000≈£3,400≈CA$6,400≈A$6,400≈S$5,800≈AED 16,500₹1,35,000flat

Answer within 48 hours

Hardening: $3,500–12,000≈€3,100–10,700≈£2,600–9,100≈CA$5,000–17,100≈A$5,000–17,200≈S$4,500–15,400≈AED 12,900–44,100₹1,05,000–3,60,000

Traditional pentests

Web, API, mobile, network, cloud and code.

The classic tests, run the same way: AI covers the surface fast, a person proves every finding, and you get a signed report and a free retest.

How a test works

Four steps, one fixed price.

The same four steps for every test. You see findings as we confirm them, not only in a PDF at the end.

  1. 1

    Scope and sign

    A free 30-minute call, then one fixed price in writing within a working day. Nothing is tested before you sign an authorization.

  2. 2

    AI covers everything

    Our tools and AI agents map every endpoint, role and AI feature in scope, and flag what looks wrong. Fast and wide.

  3. 3

    A person proves it

    A tester confirms each lead by hand, tests what AI misses (authorization, tenants and business logic) and records the evidence.

  4. 4

    Signed report, then retest

    A report and letter signed by Subcloak, a readout with your engineers, and a free retest once you've fixed things.

What AI misses

Who can see whose data?

AI testers are good at the usual web bugs. They're weakest at authorization and business logic, where SaaS breaches actually happen. So in every Proof Pentest we capture your app's real traffic with Cloak Proxy and replay every request as every role and tenant.

  • Every endpoint × every role and tenant, pass or fail, with the request as evidence.
  • The appendix auditors and enterprise buyers ask about.
  • Cloak Proxy is free, so your engineers can re-run it after every release.
About the Proof Pentest
Cloak Proxy's authorization matrix with sample data: User B gets the same data as the original user on two endpoints

Cloak Proxy's authorization matrix, with sample data.

How we work

Six promises, in writing.

Testing means trusting someone with access to your systems. These are in every contract, before we touch anything.

  • Signed authorization first

    No testing of any system until a client representative has signed a written authorization and rules of engagement.

  • Staging before production

    We test in staging or with test tenants. Production testing only with written approval and agreed limits.

  • Your data stays out of AI tools

    Client data is never sent to third-party AI services without written consent. When AI helps, it runs on zero-retention API terms.

  • Deleted after 30 days

    Working data is deleted 30 days after you accept the report, and you get a deletion certificate.

  • Fixed price, retest included

    One price agreed up front. A retest of your fixes is part of it, not an upsell.

  • Public methodology

    Our checks are published, with the standards they map to. You know exactly what you're buying.

FAQ

Testing questions

Something else? Email hello@subcloak.com or book a call.

If AI does the testing, why pay a person?

AI is fast and wide: it maps every endpoint and flags what looks wrong in hours. It is weakest exactly where breaches happen in SaaS apps: who can see whose data, across roles and tenants, and business logic. A person proves each finding, tests those paths by hand, and signs the report. Auditors and enterprise customers accept a report someone stands behind.

Will our SOC 2 auditor accept the report?

Our reports name the tester, the scope, the dates, the method and the result of the retest, and map findings to SOC 2 and ISO 27001 controls. That is what auditors look for. If your auditor has a template, send it before we start.

Do you test production?

By default we test a staging environment or dedicated test tenants. If production has to be in scope, we agree limits in writing first: rate, time windows and which actions are off limits.

Do you send our data or code to AI tools?

Not without your written consent. Our own tools run locally. When we use an AI model to help, it runs under zero-data-retention API terms, and only with your approval.

What do you need from us to start?

A signed statement of work and authorization letter, a staging URL, test accounts in at least two roles (and two tenants, if you're multi-tenant), and an engineer we can message when something needs a quick answer.

How do you price?

Fixed prices, published in full on the pricing page. You pay 50% when the work is signed and 50% on delivery. No day rates.

Get a test you can stand behind.

Thirty minutes, no slides. Tell us what you need tested and when you need the report. You'll have one fixed price in writing within a working day.