SecurityTesting
Find IDOR bugs from traffic you already captured
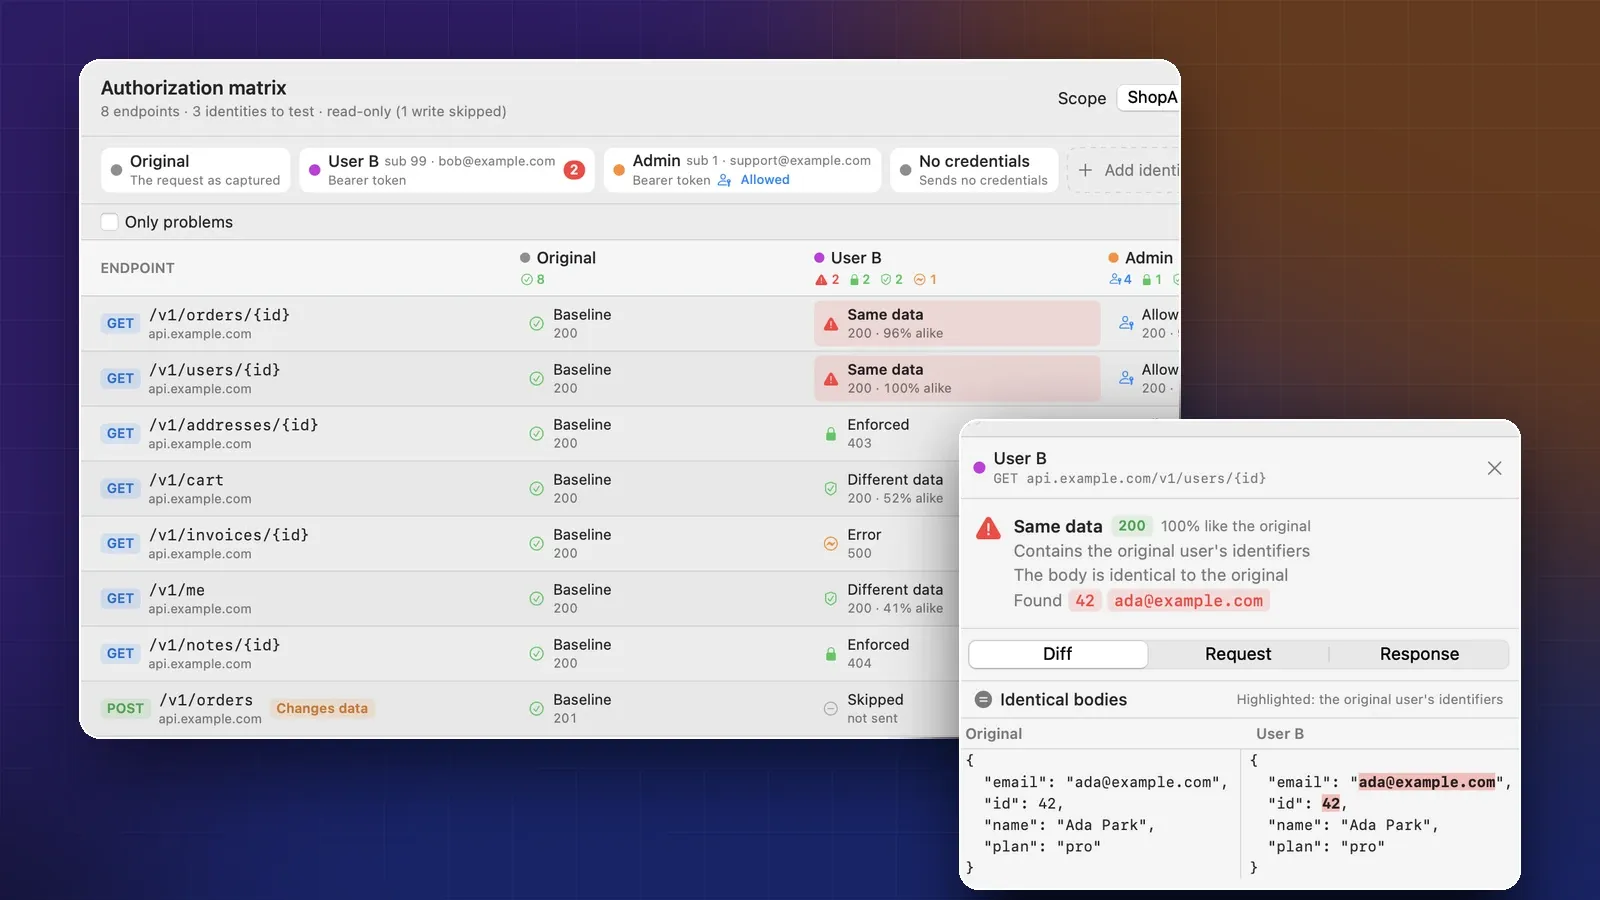
Test your own API for IDOR (broken object level authorization) by replaying captured requests as a second user, an admin and no credentials.
· 11 min read
Subcloak blog
Subcloak tests web apps, APIs and AI agents for teams that ship. Here we write up how access control breaks, how to see what an app or agent really sends, and the free tools we build along the way, such as Cloak Proxy. Real commands, sources checked.
SecurityTesting
Test your own API for IDOR (broken object level authorization) by replaying captured requests as a second user, an admin and no credentials.
· 11 min read
AI and LLMsDebugging
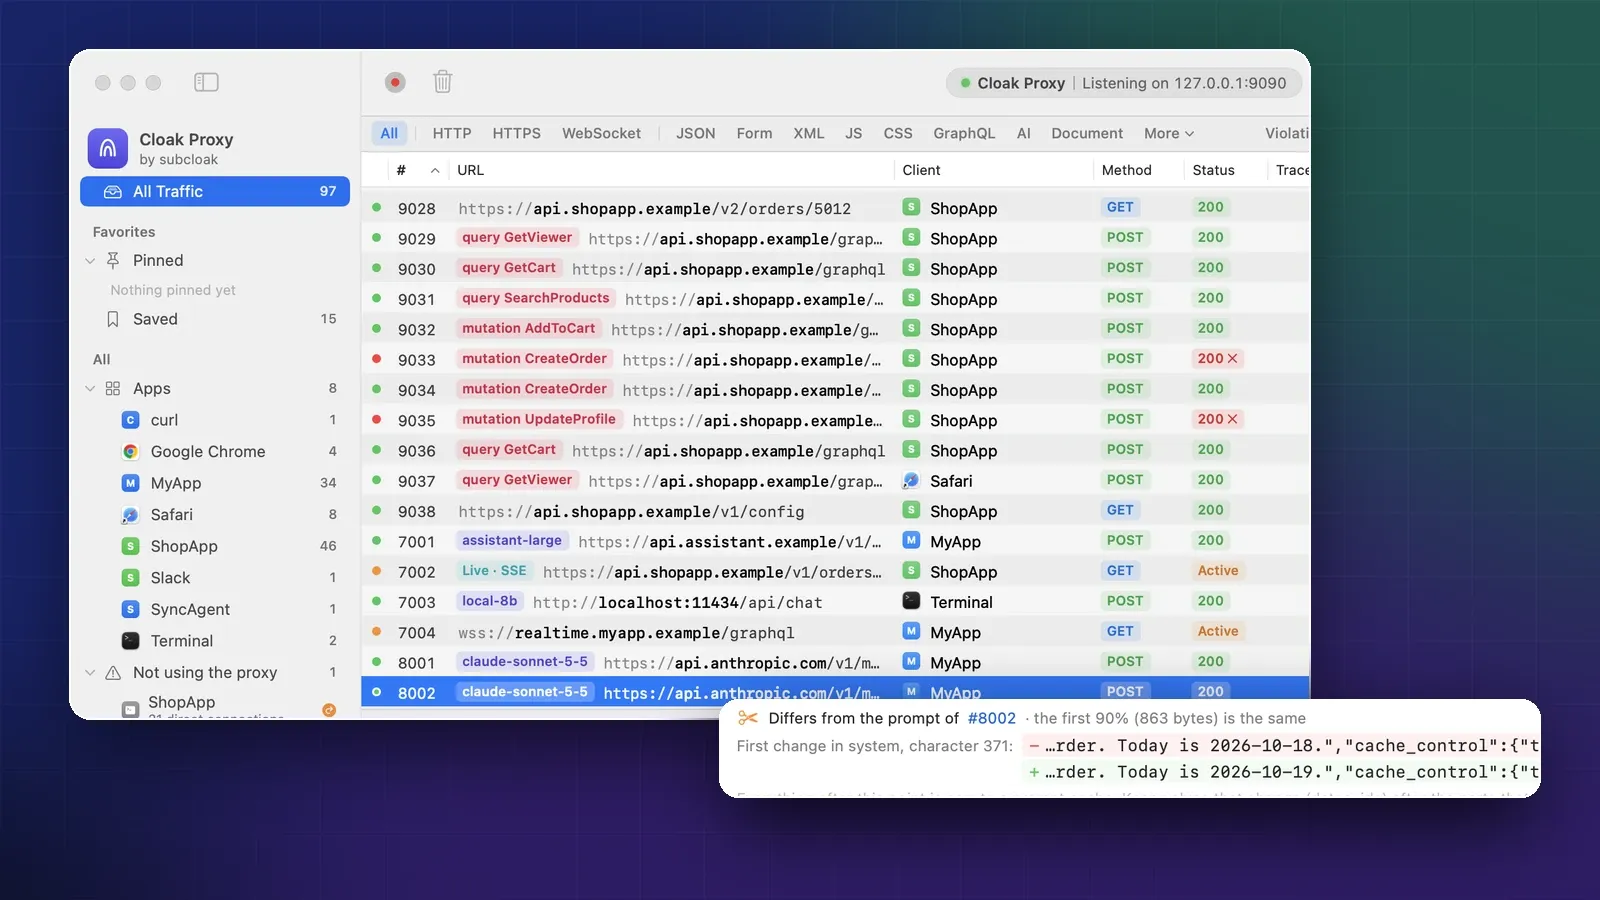
Route your agent's OpenAI, Anthropic or Gemini calls through a local proxy to see each prompt, tokens, estimated cost, time to first token and cache misses.
· 12 min read
ComparisonsDebugging
Five HTTP debugging proxies compared on price, platforms, mocking, scripting, HTTP/3, MCP and CI, with plain advice on when each one is the right pick.
· 10 min read
TestingNetworking
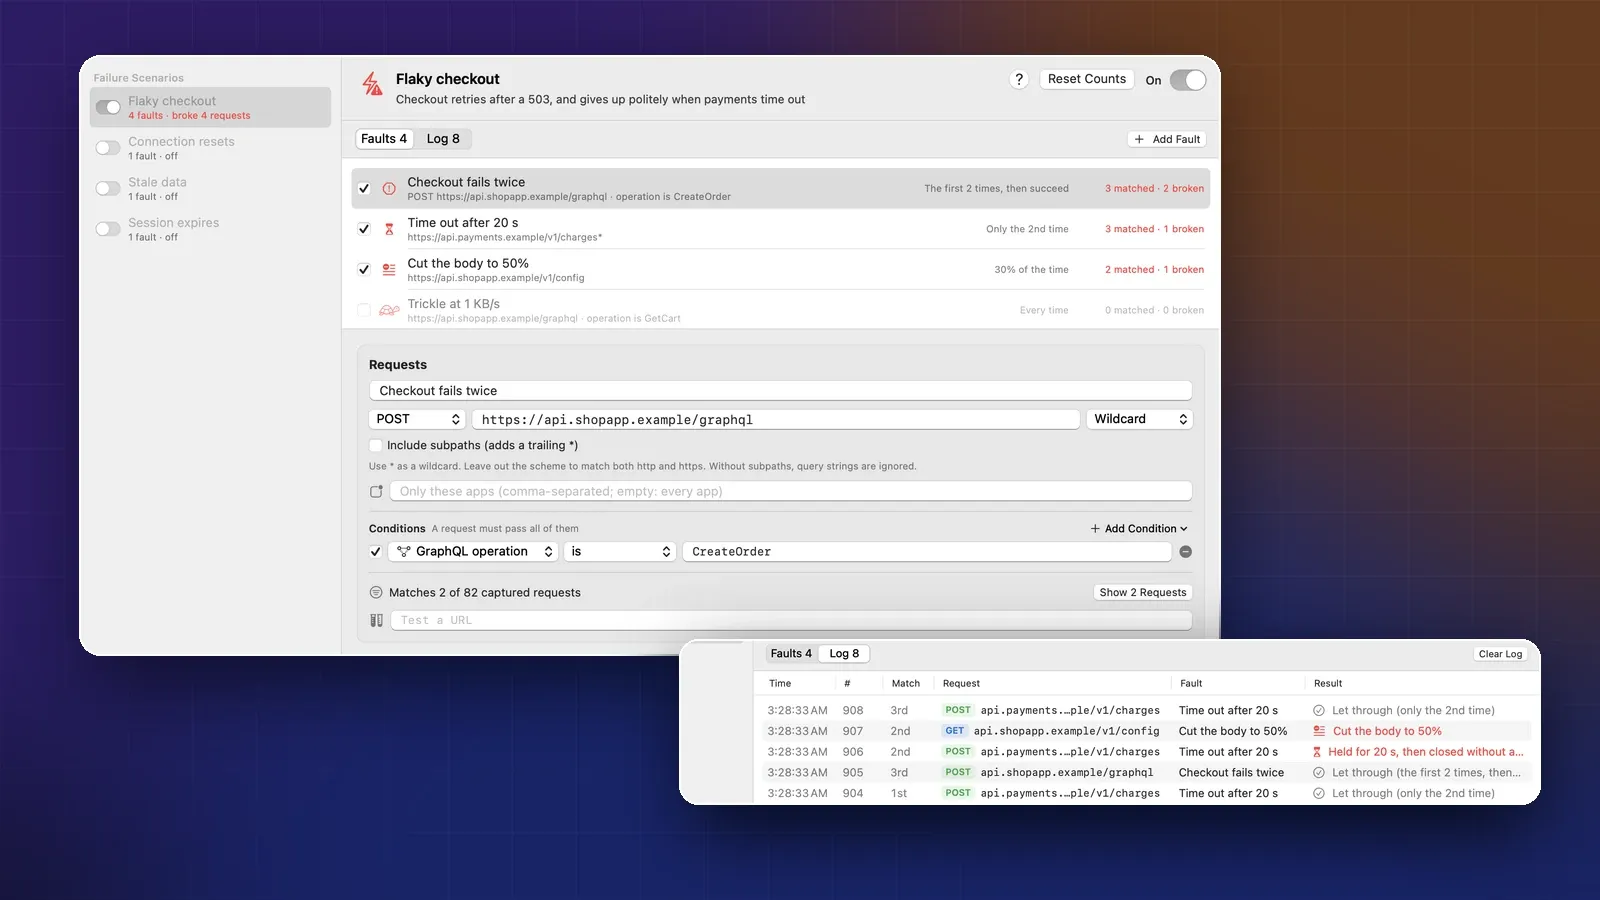
A checklist of network failures to cause on purpose: retries, timeouts, resets, cut-off bodies, slow or stale responses and expired sessions, locally and in CI.
· 11 min read
iOSMocking
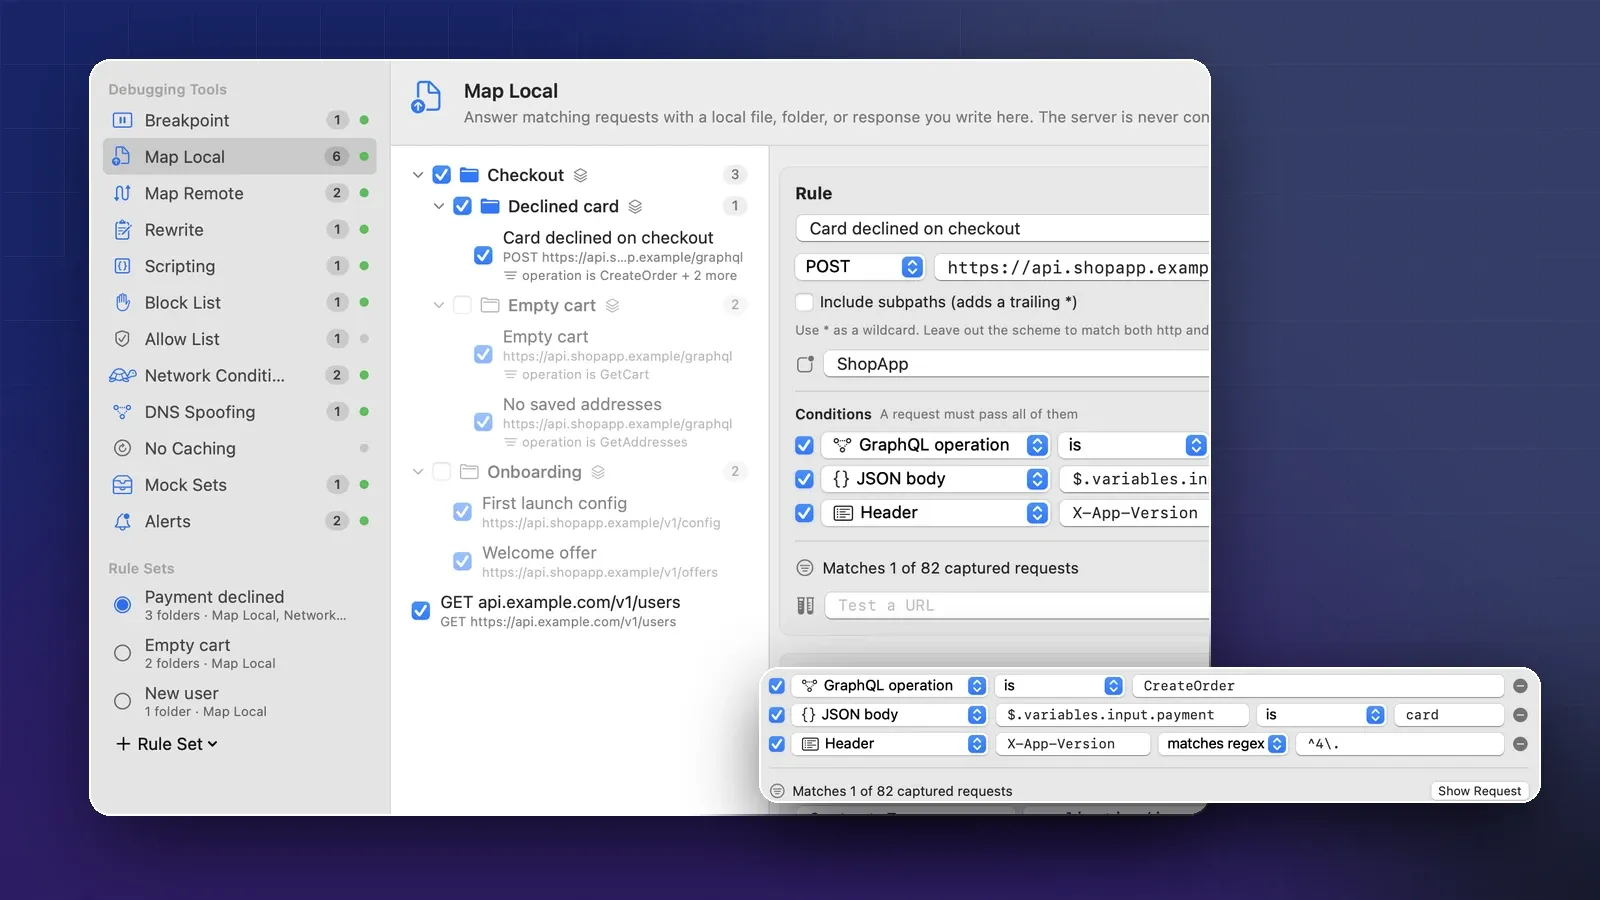
Turn a captured request into a mock, edit the JSON, and test 500s, 401s, empty lists, slow responses and single GraphQL operations, then share the mocks with your team.
· 10 min read
iOSHTTPS
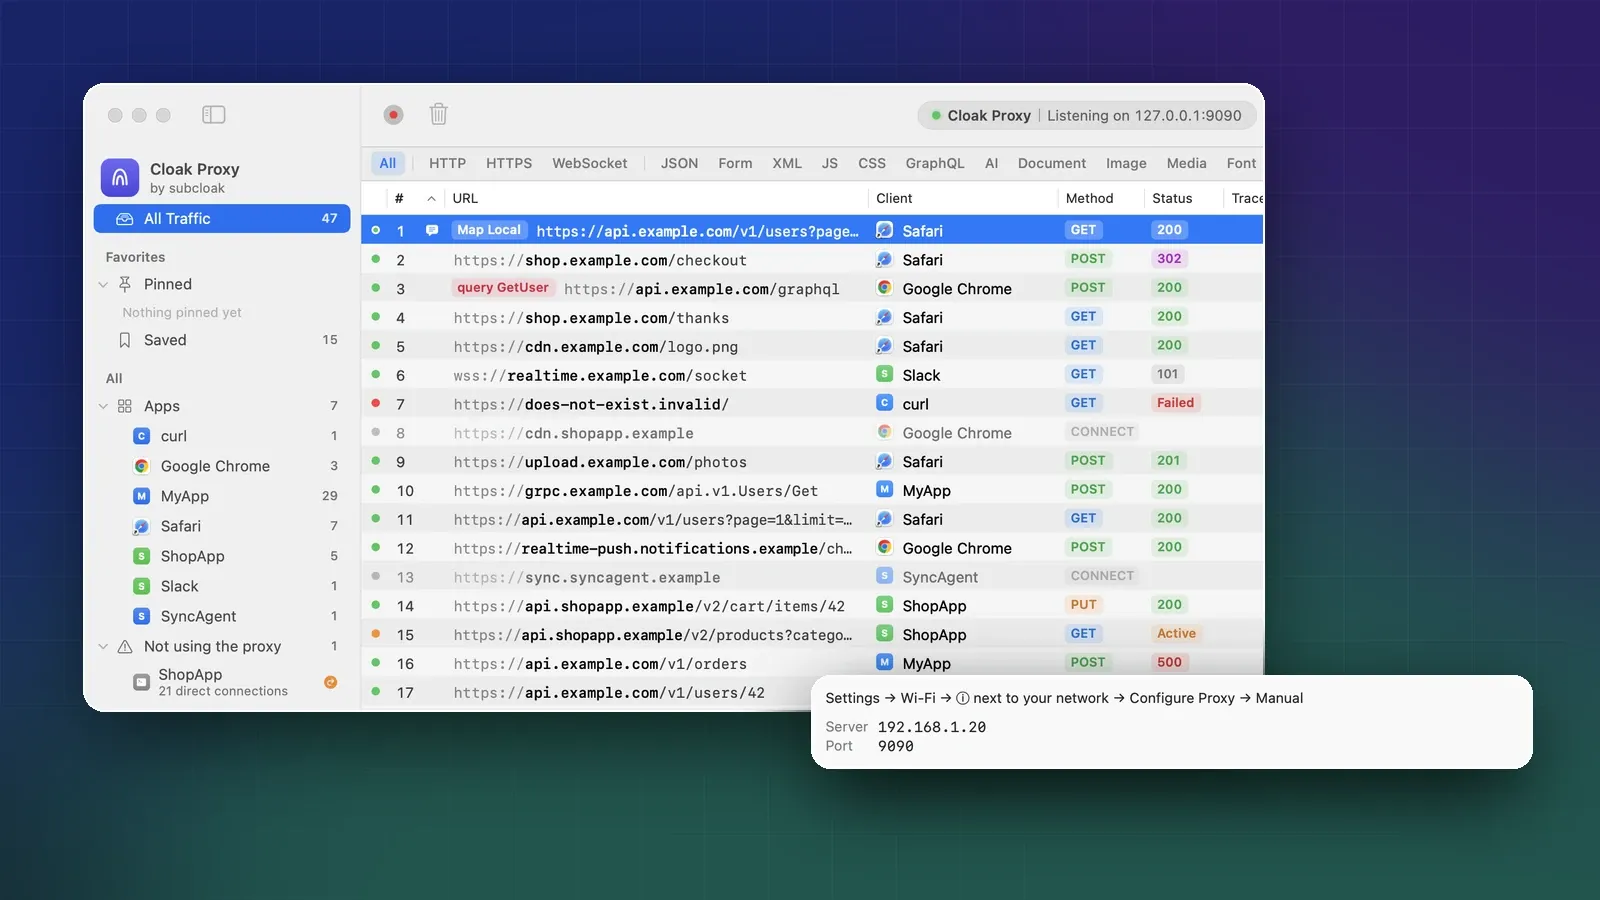
Capture and decrypt HTTPS from the iOS Simulator or a real iPhone with a free Mac proxy: setup, certificate trust, reading requests, and fixes when traffic hides.
· 12 min read
Longer studies live in Research, such as the state of MCP scopes. Follow along with the RSS feed.