Skip to content

For SOC 2, ISO 27001 and enterprise deals

The pentest your auditor accepts, proved by hand.

AI covers your whole web app and API in days. Then a person tests every role and tenant, proves each finding, and signs a report for SOC 2, ISO 27001 and your customers' security questionnaires. Report in five working days.

What you get

A signed report, and the evidence.

  • AI-driven mapping and coverage of the web app and its API
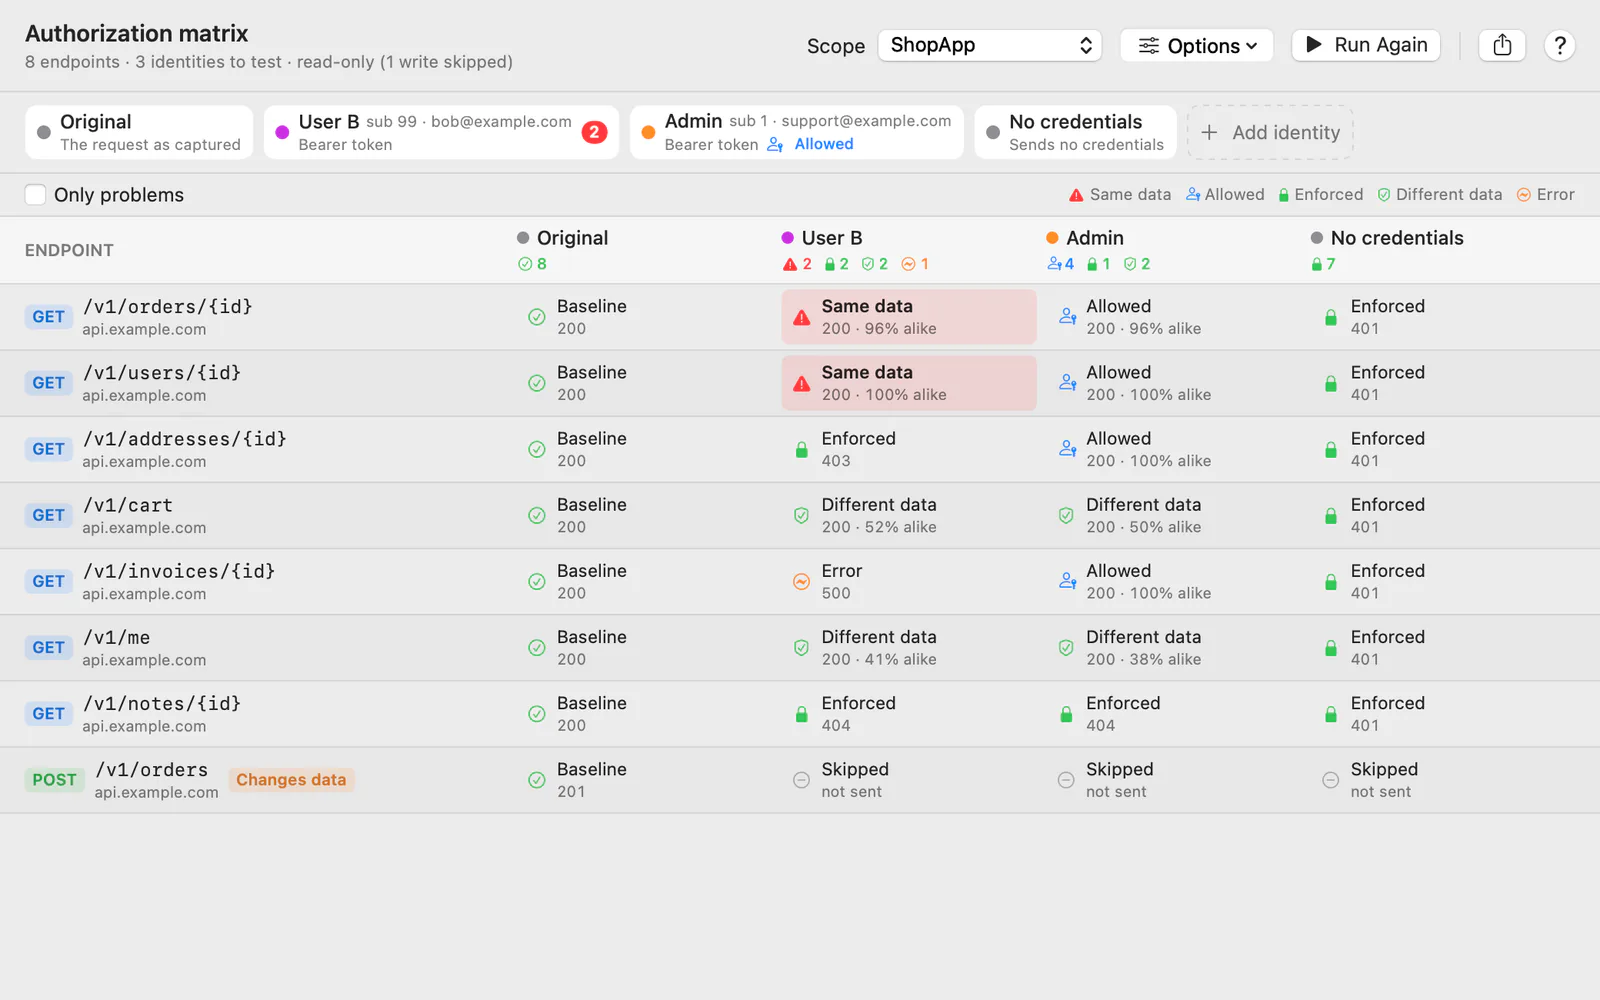
  • A role-by-role, tenant-by-tenant authorization (IDOR) matrix, built from captured traffic with Cloak Proxy
  • Human-led testing of sign-in, sessions, access control and business logic
  • Basic prompt-injection and data-leak checks on any AI feature in the app
  • A signed report mapped to SOC 2 and ISO 27001, ready for security questionnaires
  • A free retest of your fixes, and a letter your customers can verify

For: CTOs at seed to Series B SaaS companies with a SOC 2 or ISO 27001 window, an enterprise security questionnaire, or a data room to fill.

Cloak Proxy's authorization matrix with sample data: eight endpoints replayed as User B, Admin and no credentials

The authorization matrix from Cloak Proxy, with sample data. Your report includes yours: every endpoint, every role, with the request as evidence.

AI-fast, human-proven

What AI does. What a person does.

Automated testing is fast and getting cheaper. It is still weakest where SaaS breaches happen, which is why a person does that part and signs for it.

AI does

  • Maps every page, endpoint and parameter in scope
  • Probes the known bug classes: injection, XSS, SSRF, misconfiguration
  • Checks headers, TLS, dependencies and exposed files
  • Flags anything odd for a person to look at

A person does

  • Replays every request as every role and tenant: the authorization matrix
  • Tests sign-in, sessions, password reset and business logic
  • Chains small issues into the real impact, and rates severity
  • Proves each finding, writes the fix, and signs the report

See what a report looks like: sample report · verify a letter.

How it runs

Four steps, one fixed price.

  1. 1

    Scope and sign

    A free 30-minute call, then one fixed price in writing within a working day. Nothing is tested before you sign an authorization.

  2. 2

    AI covers everything

    Our tools and AI agents map every endpoint, role and AI feature in scope, and flag what looks wrong. Fast and wide.

  3. 3

    A person proves it

    A tester confirms each lead by hand, tests what AI misses (authorization, tenants and business logic) and records the evidence.

  4. 4

    Signed report, then retest

    A report and letter signed by Subcloak, a readout with your engineers, and a free retest once you've fixed things.

FAQ

Questions about this test

Something else? Email hello@subcloak.com or book a call.

Is this a real manual pentest?

Yes. AI does the wide, fast part. A person then tests sign-in, sessions, access control and business logic by hand, confirms every finding, and writes and signs the report.

What is the authorization matrix?

We capture your app's real traffic with Cloak Proxy, then replay every request as every role and tenant you give us. The matrix shows, for each endpoint, who can read or change what, with the request as evidence. It's the appendix auditors and enterprise buyers ask about, and the part automated tests miss.

Why does it include AI features?

Because most apps now have one. The Proof Pentest covers the basics: prompt injection and data leaking through any AI feature in the app. For a full test of an AI feature, add the AI Feature Security Test for $2,500.

What if our app is bigger than that?

We'll quote the extra scope on the call, as a fixed price. Larger scopes usually split into two tests.

Other tests

Need something else?

All prices

For copilots, chat, RAG, agents and MCP

AI Feature Security Test

Can your AI feature be talked into leaking another customer's data, or into using its tools in ways you never meant? We test it the way attackers do, prove the answer, and sign it.

$6,500–18,000≈€5,800–16,100≈£4,900–13,600≈CA$9,200–25,600≈A$9,300–25,800≈S$8,300–23,000≈AED 23,900–66,100₹1,50,000–3,40,000

Added to a Proof Pentest: $2,500≈€2,200≈£1,900≈CA$3,600≈A$3,600≈S$3,200≈AED 9,200₹75,000

After a supply-chain attack

Dev Environment Compromise Check

When the next npm, PyPI or AI-agent supply-chain attack hits, know within 48 hours whether it reached your developers' Macs, your CI or your secrets, then close the paths it used. Cloak Watch finds it; we fix it.

$4,500≈€4,000≈£3,400≈CA$6,400≈A$6,400≈S$5,800≈AED 16,500₹1,35,000flat

Answer within 48 hours

Hardening: $3,500–12,000≈€3,100–10,700≈£2,600–9,100≈CA$5,000–17,100≈A$5,000–17,200≈S$4,500–15,400≈AED 12,900–44,100₹1,05,000–3,60,000

Need a pentest report this month?

Thirty minutes, no slides. Tell us what you need tested and when you need the report. You'll have one fixed price in writing within a working day.