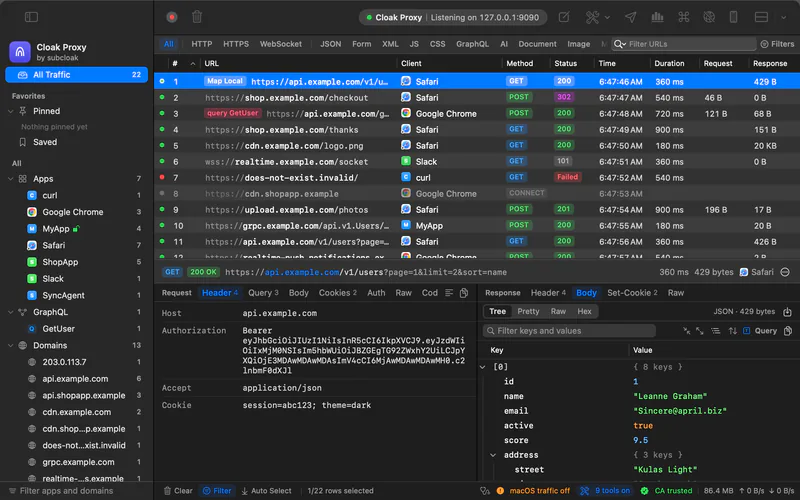
See every request your Mac makes. A native debugging proxy with an API client built in: decrypt, pause, mock and break requests, see what every model call costs, and test authorization from the traffic you already have.
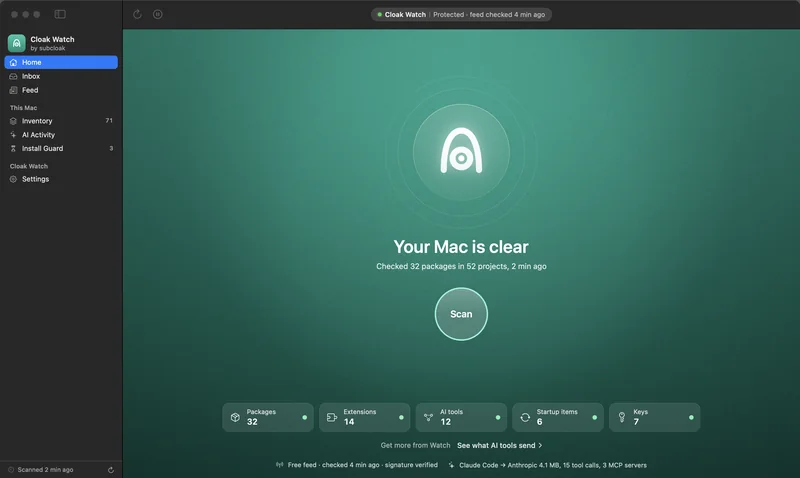
Is your Mac affected? Know in seconds. Checks packages, extensions, MCP servers, agent skills and startup items against new supply-chain attacks, and fixes what it finds in one click.
AI covers your whole web app and API in days. Then a person tests every role and tenant by hand, proves each finding, and signs the report your auditor and customers will accept.
Can your AI feature be talked into leaking another customer's data, or into using its tools in ways you never meant? We test it the way attackers do, prove the answer, and sign it.
When the next npm, PyPI or AI-agent supply-chain attack hits, know within 48 hours whether it reached your developers' Macs, your CI or your secrets, then close the paths it used. Cloak Watch finds it; we fix it.
Most testing firms buy their tools. We write ours, use them on every engagement, and give them to developers for free. Each side makes the other better.
Cloak Proxy01
Captures your app's real traffic
Every Proof Pentest replays it as every role and tenant. The result is the authorization matrix: who can see whose data, with the request as proof.
What we learn testing goes back into the apps developers get for free: Cloak Proxy's authorization matrix and its prompt-injection and MCP checks, and Cloak Watch's incident packs.
Every price is published. Tests are one fixed price agreed before we start, with a retest included.
Founding clients: Our first two AI Feature Security Test clients get 30% off in exchange for a named case study and a reference call. Open until 31 March 2027.
 Cloak Proxy, Cloak Watch